



Important Notice
What is InSight Connect?
What information do we hold about you?
How will we use your personal data and what is the legal ground we rely on for doing so?
Data Governance, Controller Status & Technical Boundaries
Law Enforcement Supply & Data Governance Policy
What happens if there is a change of purpose?
Which type of third parties might we share your personal data with?
Data retention
Where we store your personal data
No fee usually required
This policy sets out the basis on which any personal data that we process about you, or that you provide to us, will be processed by us. Please read the following explanations carefully to understand our views and practices regarding your personal data and how we will treat it and your rights.
For the purpose of applicable data protection legislation, the data controller is Portable Multimedia Limited of Floor 6, 230 Blackfriars Road London, SE1 8NW. Our company registration number is 04038169.
Our representative in the EU is Data Rep, located at 77 Camden Street Lower, Dublin D02 XE80, Ireland, https://www.datarep.com/ You can contact Data Rep on email: nextbase@datarep.com or their online web forum at www.datarep.com/nextbase
Questions regarding this policy should be directed to our Data Protection Officer who can be contacted at compliance@nextbase.co.uk. Any questions about the operation of this policy or any concerns that the policy has not been followed should be referred in the first instance to the Data Protection Officer.
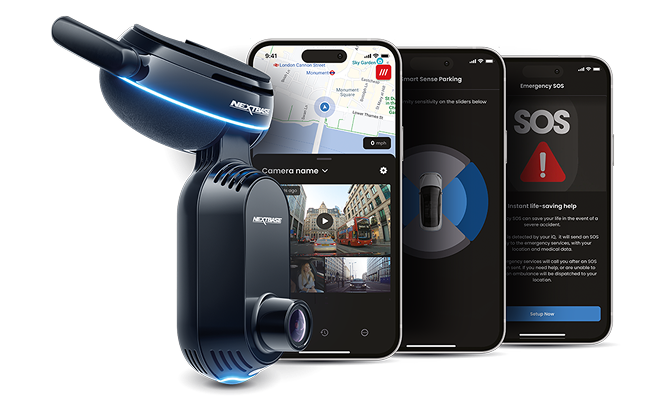
Nextbase has partnered with some fleet operators and installed LTE connected dashcams in their vehicles. The dashcams allow us to collect metadata (GPS location, date, time vector) from the cameras that allow us to create catalogues of information of footage that can be made available if they have queries about highway conditions, such as poor road surfaces, diversions, obscured road signs, damaged safety systems or mapping accuracy data.
The catalogue does not contain any video information, it is a mechanism to allow the data customer to send us a request that forms the basis of, we’re interested in something that is going on in this location, will you send us the redacted video burst from that trip that will help us understand what is going on / means we don’t have to send our own vehicle to check this.
We shall ensure that members of the public are informed about the fleet partners with whom we have established partnerships either by means of notices on vehicles included in the scheme or by means of public webpages that provide information on the business we are working with.
The accuracy of the redaction process that occurs in the camera by destroying the pixels that would form faces of license plates in images to be shared, is very accurate but we recognise that some personal data may remain. Therefore, we are issuing this Privacy Notice so that you can be informed about how we process the data that we capture.
We may collect, store and use information about you (referred to throughout this privacy policy as personal data):
Where Nextbase hardware and cloud infrastructure are deployed across host enterprise fleets under InSight Connect:
· Short bursts or streams of video footage capturing the external road environment and surroundings.
· Metadata including GPS location coordinates, vehicle speed, timestamp, time/date, and hardware telemetry.
· InSight Connect does not collect or retain internal cabin audio or driver-facing video. Any fleet product or feature involving in-cabin audio or video is separate from InSight Connect and is governed by its own privacy notice.
InSight Connect is not designed to identify individual drivers or monitor driver behaviour. Meta data is collected to enable us to construct data catalogues to show data customers what is available. This in turn enables us to limit the quantity of video data requested from cameras and only transfer data to meet a specific request from data customers subject to controls listed in Section 3.
We will only process your personal data when the law allows us to. When we process your personal data, we must have a legal ground for doing so. The legal grounds by which we can use your personal data:
a) Where it is in pursuit of our legitimate interests (or those of a third party) and your interests and fundamental rights do not override those interests
b) For the establishment, exercise or defence of legal claims
| Data Use Case | UK GDPR clause | EU GDPR clause | AUS Privacy Act 1988 Privacy Principles | NZ Privacy Act 2020 Privacy Principle |
| a | Art. 6 (1) (f) | Art. 6 (1) (f) | APP 6.2 (c), 16A, 1 (a) (a) | IPP 11 1 (a), (h) (i), IPP 12 (1) (c) |
| b | Art. 17 (1) (e), 18 (1) (c), 21 (1), 49 (1) (e) | Art. 17 (1) (e), 18 (1) (c), 21 (1), 49 (1) (e) | APP 6.2 (c), 16A, 2 (a) (a) | IPP 10 (1) (e) (i, ii, iii, iv), IPP 11 (1) (e) |
More specifically, we will process your personal data in the following circumstances:
· Short bursts, telemetry, and environmental road video collected via InSight Connect hardware and cloud infrastructure provided to host businesses – to fulfil legitimate interests we have in sharing video of the highway environment with data customers, to improve the highway environment and mapping services.
Data Controller Role (InSight Connect)
· Under the InSight Connect ecosystem, Nextbase acts as a Data Controller or Joint Controller (alongside or independently of the host fleet operator). Nextbase does not act as a data processor for the fleet operator. Nextbase independently determines the purposes and technical means of processing, aggregating, anonymising, and distributing environmental geospatial datasets.
Automated Redaction at Source & ANPR Prohibition
· Nextbase operates strictly on Privacy-by-Design and Privacy-by-Default principles:
o Edge Redaction: All video captured by InSight hardware undergoes automated edge-redaction at source prior to cloud transmission or telematics aggregation. On-device algorithms automatically detect and destroy pixels that would form detected faces and vehicle registration marks.
o Prohibition of ANPR: We do not use facial recognition or biometric identification in InSight Connect. Nextbase does not, and will not, deploy Automatic Number Plate Recognition (ANPR) technology. Hardware and edge processing algorithms actively destroy pixels containing vehicle number plate digits
and facial features at source. The redaction is designed to prevent the resulting imagery from being used for optical character recognition (OCR) or number-plate indexing.
Architecture & Query Throttling (Anti-Surveillance Safeguard):
· InSight Connect operates via a two-tier privacy-by-design architecture:
o Cloud Catalogue Layer: Devices upload non-identifying telemetry and index metadata to a cloud catalogue to allow data customers to identify relevant road infrastructure segments. Video footage is not mass-uploaded to central cloud storage.
o Targeted Data Extraction: Video is transmitted only in short bursts in response to specific, parameter-driven queries against the catalogue.
o Technical Rate-Limiting & Anti-Tracking Controls: To prevent the potential monitoring or tracking of vehicle movements, Nextbase enforces hard technical rate limits on data requests per individual vehicle. High-frequency or consecutive data pulls from a single device are systematically blocked by system architecture.
Nextbase maintains a strict governance framework regarding Law Enforcement Agencies (LEAs), judicial requests, and official criminal investigations.
Commercialisation Boundary
· Nextbase does not commercialise, licence, sell, or package imagery, telemetry, or personal data from its InSight program or consumer platforms to Law Enforcement Agencies. The InSight platform is maintained strictly as an infrastructure, mobility, and geospatial enhancement framework.
Remote Device Access & Law Enforcement Requests
Nextbase does not provide Law Enforcement Agencies with remote access to InSight devices. Where Nextbase receives a valid law-enforcement request, it will assess and respond only in relation to personal data that it holds or controls. Any request for locally stored material must be directed to the relevant vehicle owner or Fleet Operator and is outside Nextbase's control.
· Remote 4G LTE Capabilities & Scope: InSight Connect devices possess 4G LTE connectivity allowing for remote access. However, Nextbase does not proactively capture or continuously extract data via this connection. Remote retrieval is carried out strictly on an ad-hoc basis upon specific data requests from authorized data customers. Requests are made based on data catalogues that contain no images.
· Exclusion of Crash / Accident Footage: Accident and crash footage is not requested, targeted or included in InSight Connect mapping and infrastructure datasets.
· Law Enforcement Access Requests: Law Enforcement Agencies seeking access to footage stored on or accessible via a device must submit a valid legal power or other lawful authority applicable to the circumstances in which InSight Connect is operating to Nextbase through official law enforcement channels. The requesting agency must provide specific details regarding the precise nature and legal basis of the request and why access to or extraction of the data is required.
· Physical SD Cards: Law Enforcement Agencies seeking local footage may obtain direct physical access to the SD card or hardware directly from the vehicle owner or Fleet Operator under applicable legal powers of seizure. The data on the card is encrypted. Nextbase does not provide encryption keys or routine means of bypassing that encryption
Device Seizure & Encryption Key Governance
Where law enforcement lawfully obtains physical possession of a device or SD card, Nextbase does not voluntarily disclose encryption keys or otherwise provide routine means of bypassing the encryption.
o Encryption Key Control: Nextbase maintains a policy that we do not voluntarily disclose encryption keys to third parties or Law Enforcement Agencies. Any legally binding demand for disclosure would be referred to Legal and challenged where appropriate. Encryption keys remain under the sole and exclusive ownership and control of Nextbase.
o File-Level Cryptography & Firmware: Every file recorded on Nextbase hardware is encrypted individually. Firmware updates systematically enforce file-level re-encryption, this is intended to prevent unauthorized key harvesting or hardware reverse-engineering.
o Systemic Security Integrity: Withholding encryption keys protects the cryptographic security architecture across the entire global Nextbase device fleet.
We will only use your personal data for the purposes for which we collected it, unless we reasonably consider that we need to use it for another reason and that reason is compatible with the original purpose. If we need to use your personal data for an unrelated purpose, we will notify you, explain the legal basis which allows us to do so and obtain your consent where required.
We require third parties to respect the security of your personal data and to treat it in accordance with the law. For example, where we instruct third party service providers, we carry out due diligence on those providers to ensure they treat your personal data as seriously as we do.
We may share your personal data with the following types of third parties:
· Providers which help us collate and organise information effectively and securely.
· Third party software hosting companies which provide us with software solutions.
· Providers which host our servers in their data centres (these are within Ireland for UK, EU, and in the USA for North America, there is also a server in Australia).
How long will we use your personal data for?
We will only retain your personal data for as long as necessary to fulfil the purposes we collected it for.
We assess the appropriate retention period for different information based on the size, volume, nature and sensitivity of that information, the potential risk of harm to you from unauthorised use or disclosure of that information, the purposes for which we are using that information, applicable legal requirements for holding that information, and whether we can achieve those purpose(s) through other means.
Electronic versions of any personal data collected in the UK/EU are stored on AWS servers in Ireland. To limit international transfers, we also have server capability in the USA for North American. Additionally there is a server in Australia for iQ customers.
Where we use third party service providers to assist us, your personal data may also be stored in accordance with their practices and procedures. We require third parties to respect your personal data and to treat it in accordance with the law.
Where your personal data are transferred outside of the EEA, we will take steps to ensure your personal data is adequately protected, by confirming that the partner has conducted data protection assessments and / or abides by the requirements of the GDPR. Please contact our data protection officer for more information.
Video data and metadata related to the videos that dash cams send to the cloud (only applies to connected devices) will be stored on AWS servers in the United States for customers in North America and in Australia for customers in Australasia. This ensures users benefit from better connection speeds for big data sets.
Rights of access, correction, erasure, restriction, portability and objection
Your rights in connection with your personal data
Under certain circumstances, by law you have the right to:
· Request access to your personal data (known as a “data subject access request”). This enables you to receive a copy of the personal data we hold about you and to check that we are lawfully processing it.
· Request correction of the personal data that we hold about you. This enables you to have any incomplete or inaccurate information we hold about you corrected.
· Request the erasure of your personal data. This enables you to ask us to delete or remove personal data when there is no good reason for us continuing to process it. You also have the right to ask us to stop processing personal data where we are relying on a legitimate interest and there is something about your particular situation which makes you want to object to processing on this ground.
· Request the restriction of processing of your personal data. This enables you to ask us to suspend the processing of personal data about you, for example if you want us to establish its accuracy or the reason for processing it.
· If you want to exercise any of the above rights, please contact our Data Protection Officer in writing or by telephone using the contact details set out at the beginning of this privacy policy.
You will not have to pay a fee to access your personal data (or to exercise any of the other rights). However, we may charge a reasonable fee to the extent allowed by applicable law if your request for access is clearly unfounded or excessive. Alternatively, we may refuse to comply with the request in such circumstances.
We may need to request specific information from you to help us confirm your identity and ensure your right to access any personal data (or to exercise any of your other rights). This is a security measure to ensure that personal data is not disclosed to another person who has no right to receive it.
Nextbase conducts in camera redaction to destroy the pixels in images that would have formed identifiable faces or licence plates. Whilst this screening is highly accurate, we cannot claim that it will always be free of all personal data.
We acknowledge that we have not received your consent to process your data. It is not technically feasible to receive your consent (images including but not limited to your face, your vehicle license plate, and similar data that would enable the identification of a unique living individual) where we have no direct relationship with you. Nevertheless, you still have rights
If you are concerned about data that has been collected that may contain unredacted images of you, you can request the removal of your data by contacting our Data Protection Officer or data protection representative in writing using the contact details set out at the beginning of this privacy policy.
Once we have established that you are the owner of the data, we will as a start point ensure that you are removed from the specific footage as defined by date, timestamp and GPS location, unless required by law. Note that it shall be necessary to issue an access request for each occasion where you are concerned that we have included your image in redacted data sets that we can have shared with data customers.
If you fail to provide certain information when requested, we may be prevented from complying with our legal obligations (such as to assist with a data subject access request).
You have the right to make a complaint if you wish to do so.
In the first instance, please direct complaints to our Data Protection Officer who can be contacted at compliance@nextbase.co.uk.
If we cannot resolve your complaint, you can complain to the regulator. The regulator in the UK is the Information Commissioner’s Office, which can be contacted in writing at Information Commissioner’s Office, Wycliffe House, Water Lane, Wilmslow, Cheshire, SK9 5AF, by telephone (0303 123 1113) or by e-mail (casework@ico.org.uk) or your own data protection agency.
We are based in the UK but, under the EU GDPR, we are required to appoint an EU representative. The purpose an EU representative is to make it easy for individuals located in the EU to contact us should they wish to exercise their rights or make a complaint or enquiry in relation to how we are processing their Personal Data. It is also a contact point for the supervisory authorities located in the EU.
Our EU representative is Data Rep
You can contact Data Rep on email: nextbase@datarep.com or their online webforum at www.datarep.com/nextbase
If you are resident in Australia, or you are an Australian citizen you may contact The Office of the Australia Information Commissioner (OAIC), by post at GPO Box 5288, Sydney NSW 2001, by telephone (1300 363 992) or via the OAIC’s website https://www.oaic.gov.au/privacy/privacy-complaints
If you are resident in New Zealand, you may contact the Office of the Privacy Commissioner Te Mana Mātāpono Matatapu by post at PO Box 10 094, Wellington 6143, by telephone 0800 803 909 (Monday to Friday, 10am to 3pm) or by email (enquiries@privacy.org.nz).
Residents in the United States of America may contact privacy officers at the following addresses
| California | https://cppa.ca.gov/ |
| Colorado | https://coag.gov/ |
| Connecticut | https://portal.ct.gov/dcp/ |
| Delaware | https://attorneygeneral.delaware.gov/fraud/personal-data-privacy-portal/ |
| Florida | |
| Iowa | |
| Montana | |
| Nebraska | https://protectthegoodlife.nebraska.gov/data-privacy-homepage |
| New Hampshire | |
| New Jersey | https://www.njconsumeraffairs.gov/ocp/Pages/NJ-Data-Privacy-Law-FAQ.aspx |
| Oregon | https://www.doj.state.or.us/consumer-protection/id-theft-data-breaches/privacy |
| Texas | |
| Utah | |
| Virginia | https://department.va.gov/privacy/ |
The Canadian regulator.
| Alberta | https://www.alberta.ca/personal-information-protection-act |
| British Columbia | https://www.oipc.bc.ca/about/commissioner/ |
| Manitoba | https://www.ombudsman.mb.ca/ |
| New Brunswick | https://ombudnb.ca/ |
| Newfoundland and Labrador | https://www.oipc.nl.ca/ |
| Northwest Territories | https://oipc-nt.ca/ |
| Nova Scotia | |
| Nunavut | |
| Ontario | |
| Prince Edward Island | https://www.assembly.pe.ca/offices/information-and-privacy-commissioner |
We may change, modify, add or remove portions of this policy at any time, and any changes will become effective immediately.
Any changes we make to our privacy policy will be posted on this page and, where appropriate or required, notified to you.